Carsensor services report possible exposure of up to 3,709,551 personal-data records
The operator’s October 21 announcement and ITmedia’s 12:41 JST report describe possible exposure and a maximum count, not confirmed leakage of every record.
 Illustration
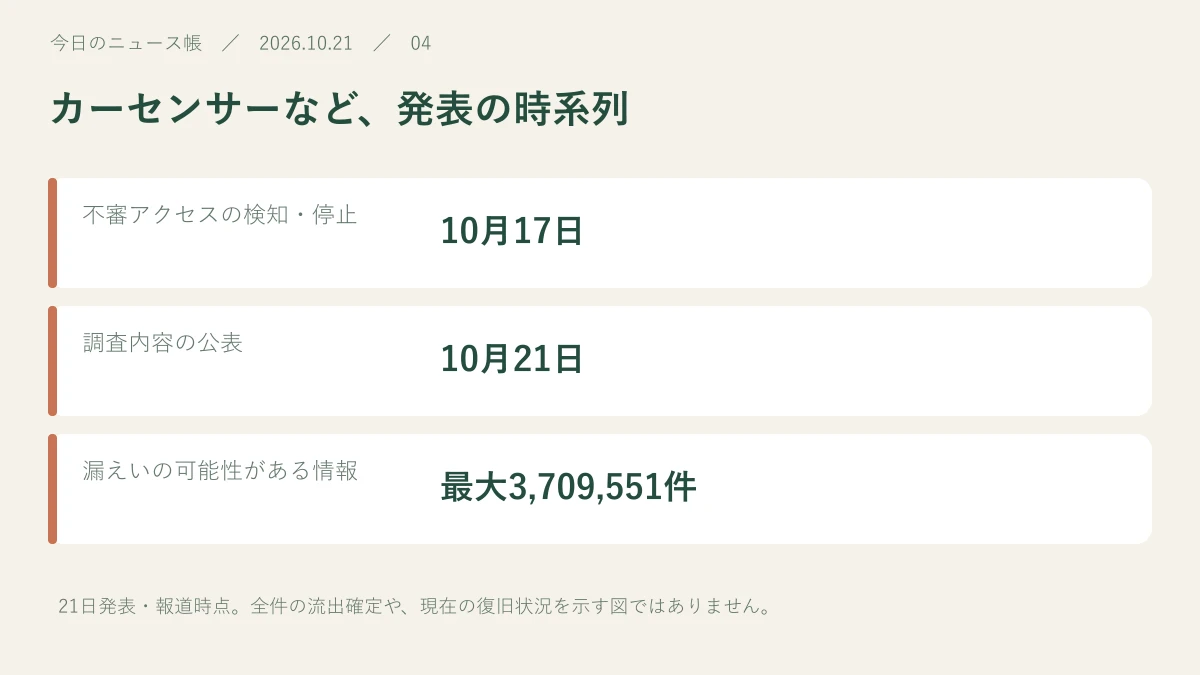
Recruit announced on October 21 that unauthorized access to Carsensor net and dealer service C-MATCH may have exposed up to 3,709,551 records. Related services had been suspended after suspicious access was detected on October 17.
Read for 8 seconds to inform recommendations.Reading history & counting settings
The operator’s October 21 announcement and ITmedia’s 12:41 JST report describe possible exposure and a maximum count, not confirmed leakage of every record.
Investigation followed the October 17 suspension
According to ITmedia, Recruit detected suspicious access on October 17 and suspended related services around 17:00 that day. Its investigation identified possible data categories and counts by October 20, which it disclosed on October 21. The services are Carsensor net and C-MATCH.
A maximum potential count is not a confirmed total
The figure of up to 3,709,551 covers personal information of users and business contacts that may have leaked. Reporting includes enquiry customers’ names and addresses. It does not establish confirmed exposure of every record. Individual applicability, guidance and subsequent service status should be checked in official announcements.
Sources & further reading
Our own summary based on the public information below.
- リクルート:カーセンサーnet・C-MATCHへの不正アクセスに関するお知らせ ↗Source publication date: 2026-10-21
- ITmedia:最大370万9551件の漏えいの可能性 ↗Source publication date: 2026-10-21
This is a record of information available at publication. Later reports may change the details. Check the source for current weather, safety and market information.